 Gateward
WordPress firewall
Every request checked. Every attack explained.
Gateward is a web application firewall that runs on your own server, before other plugins load. It blocks attacks, bans repeat offenders on an escalating ladder and shows you, in plain English, which requests are safe and which are dangerous.
Free on WordPress.org
A complete firewall, not a teaser
Everything below is in the free plugin.
Attack rules
SQL injection, XSS, code execution and path traversal in URLs, forms, headers and cookies. Sensitive-file probing, scanners, user enumeration, 404 floods.
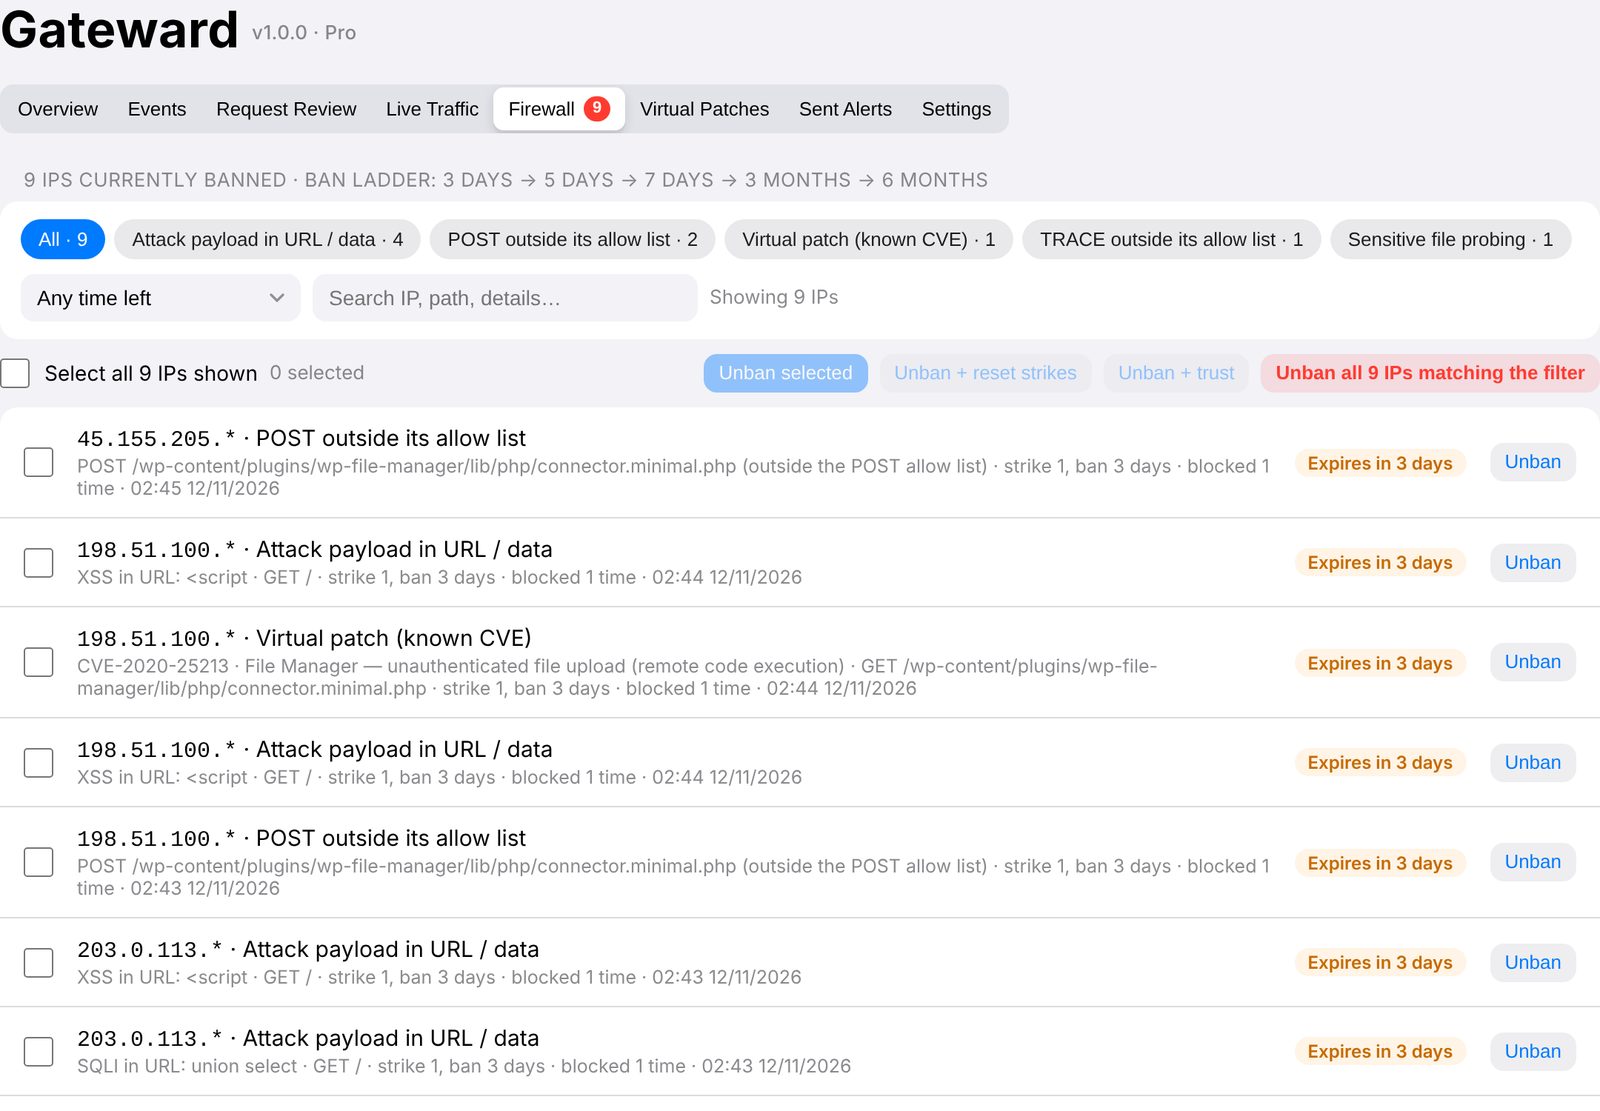
Escalating bans
Repeat offenders stay out longer. No permanent bans, multi-select unban, and people sharing an IP can still read your site and log in.
Runs first
One click loads the firewall before any other plugin, so exploits against vulnerable plugins are stopped before their code runs.
Bot challenge, no CAPTCHA
Rate limits per IP and an "Under attack" mode: browsers solve a one-second proof-of-work check, bots don't.
Real bots in, fake bots out
Googlebot, Bingbot, Applebot and others are verified by DNS. Impostors are blocked; real crawlers skip rate limits so your SEO is safe.
Login hardening
Custom login address, lockouts that escalate to bans, one generic error message, and alerts for admin logins from unknown networks.
Request Review
Is this request safe? Gateward tells you why.
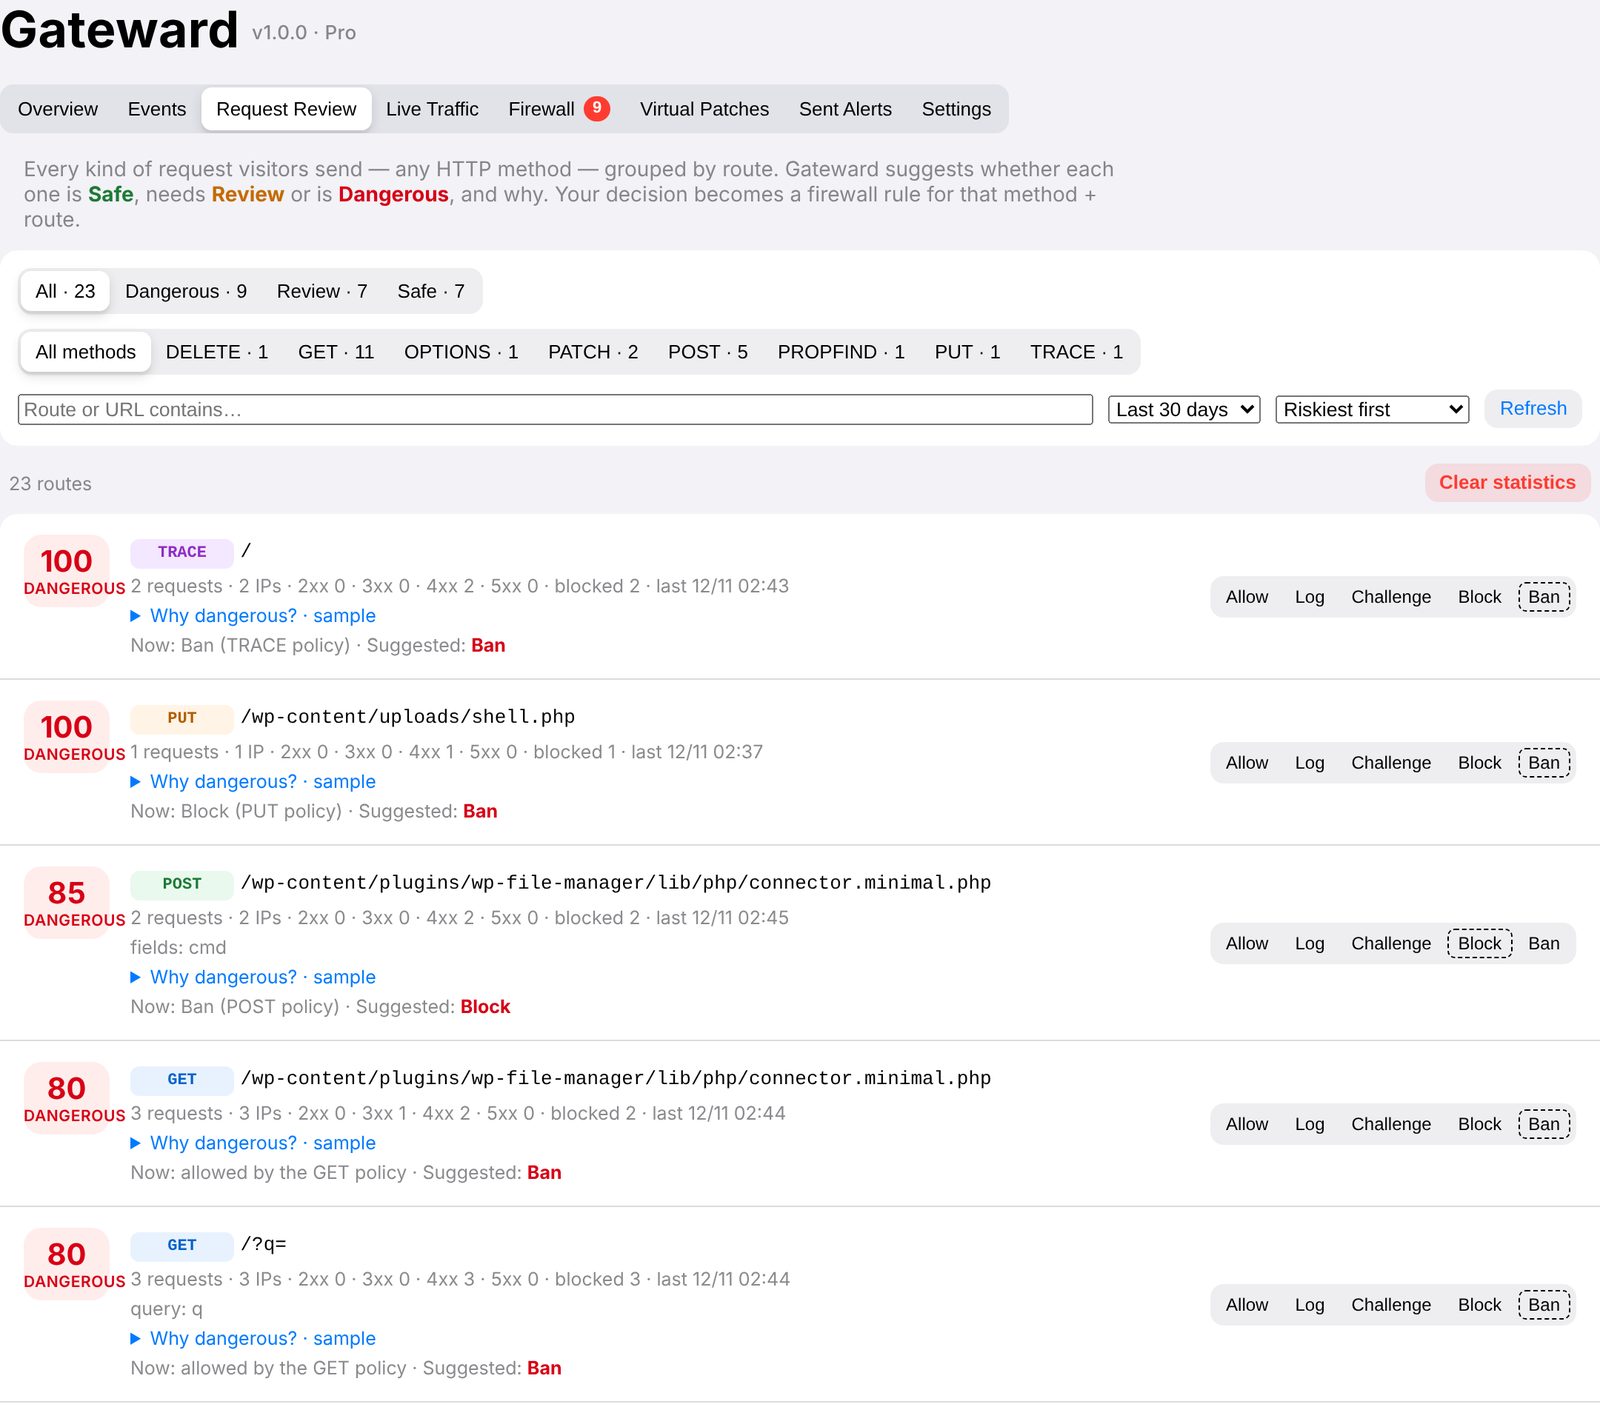
Every kind of request visitors send — any HTTP method — is grouped by route and scored Safe, Review or Dangerous, with the reasons. One click turns your decision into a firewall rule.
- Spots webshell paths, serialized objects, REST routes no plugin registers and AJAX actions that don't exist
- Allow, Log, Challenge, Block or Ban per method and route
- A few attacks never condemn a route real visitors use
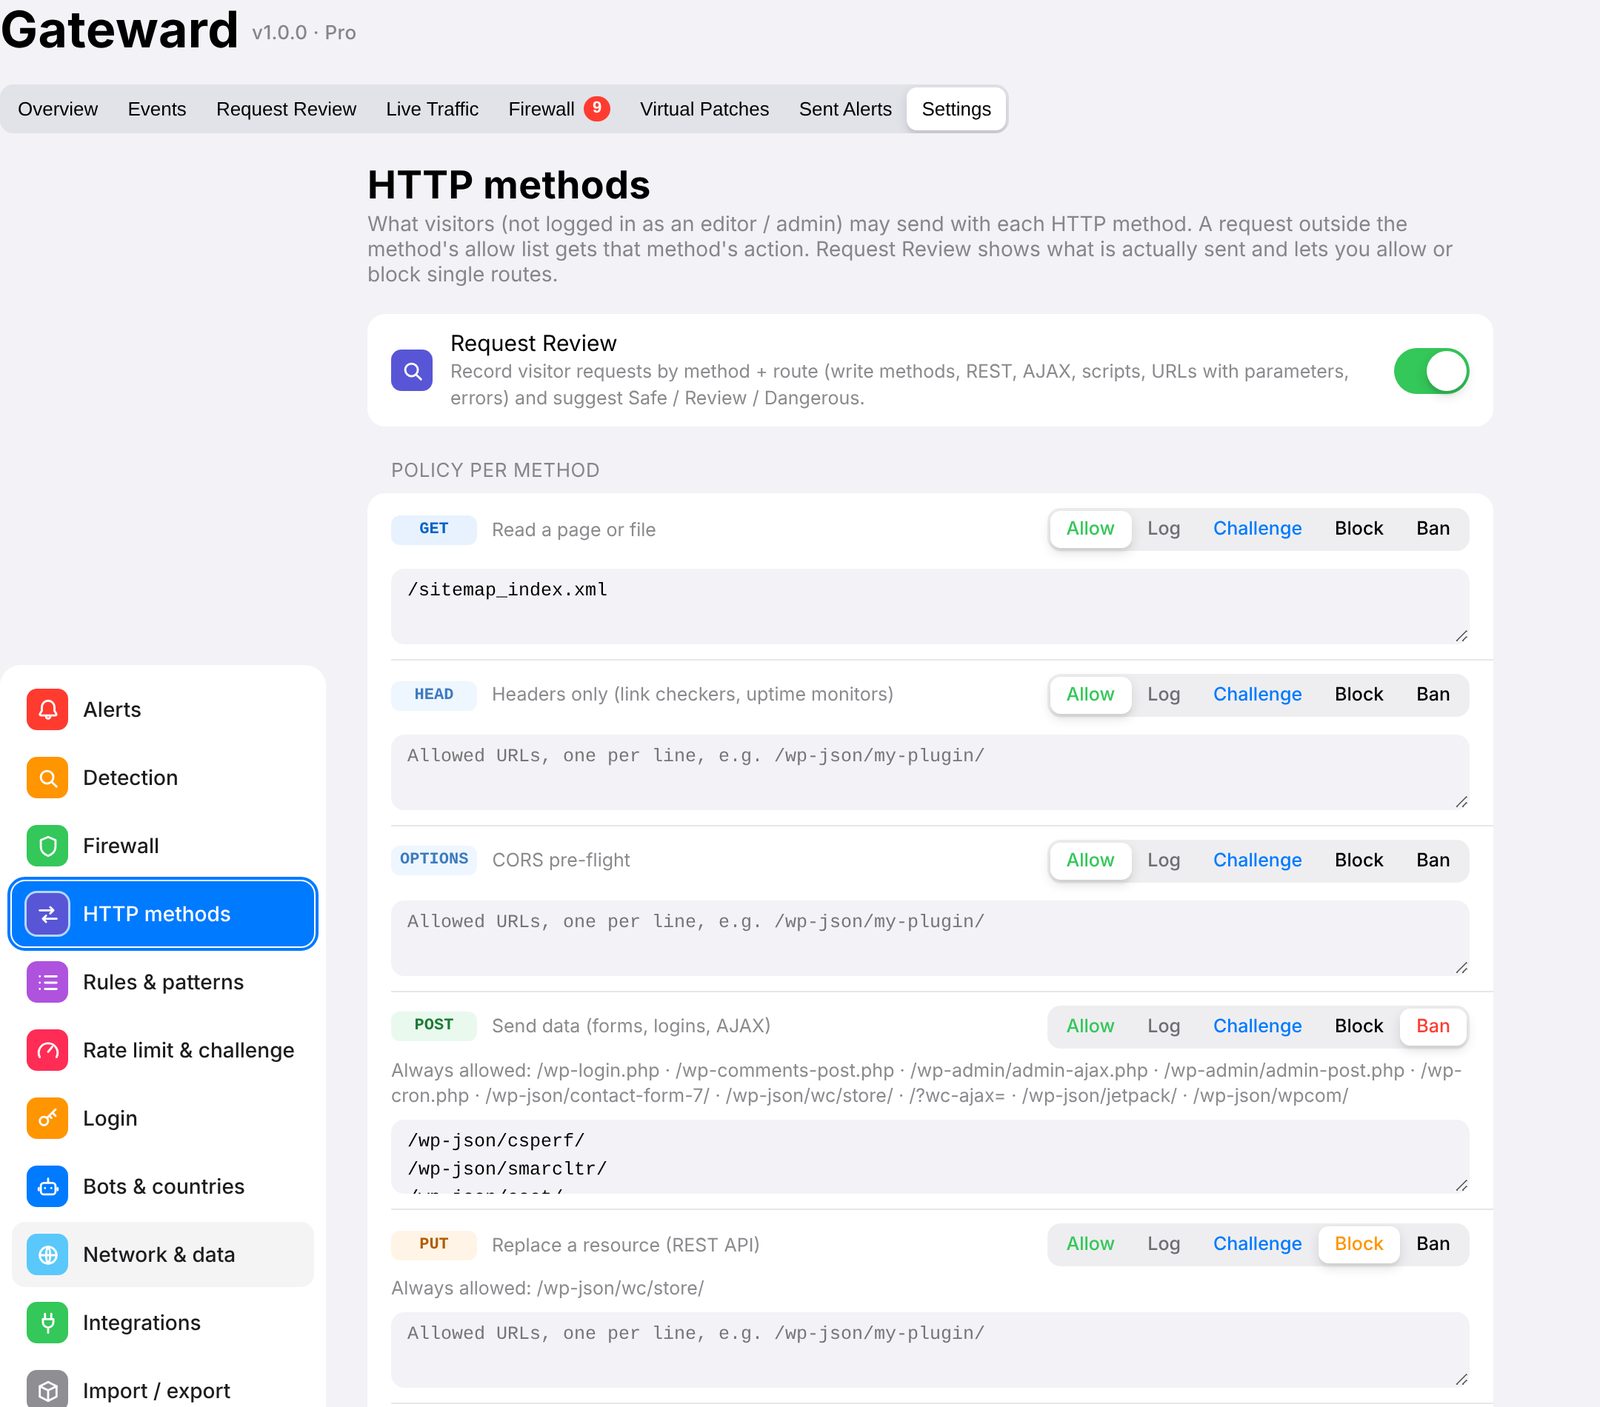
Every HTTP method
GET to CONNECT, each with its own policy
Set what visitors may send with each method and keep an allow list per method. TRACE and CONNECT are banned out of the box; REST method overrides are judged by the real method.
GETHEADOPTIONSPOSTPUTPATCHDELETETRACECONNECTPROPFIND…
Gateward Pro
When you can't update today
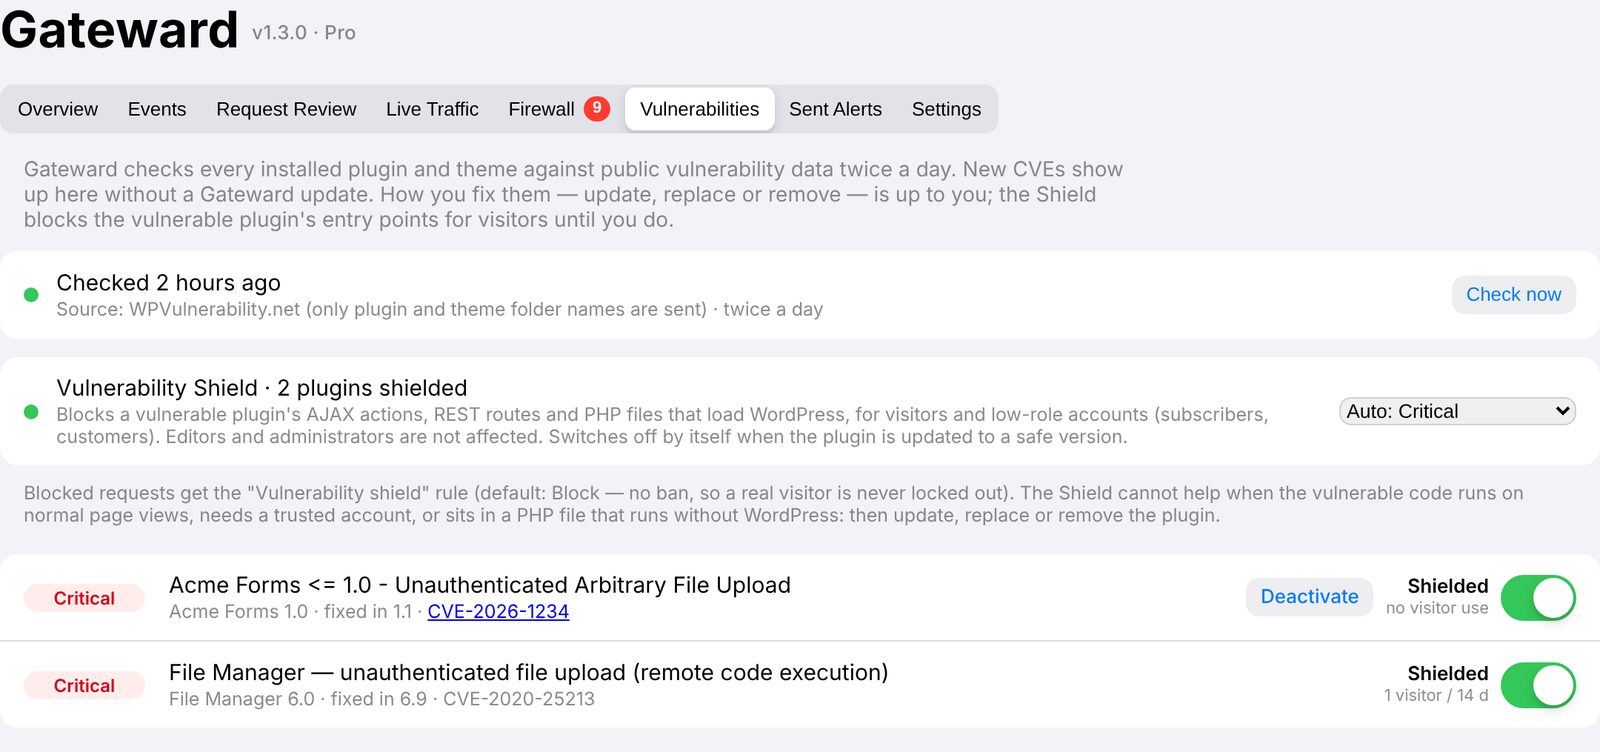
Gateward checks your plugins and themes against public vulnerability data twice a day and tells you when one has a known CVE — free. You decide how to fix it. If you can't update right away, Gateward Pro keeps attackers away from that plugin in the meantime.
Shield vulnerable plugins
Closes a vulnerable plugin's AJAX actions, REST routes and PHP files that load WordPress to visitors until you update. Editors keep working, and the Shield switches off after the update.
Slack, Teams, Discord, Telegram, Zalo
Alerts reach your team the moment they happen, plus signed JSON webhooks and a weekly report.
Watch requests as they happen
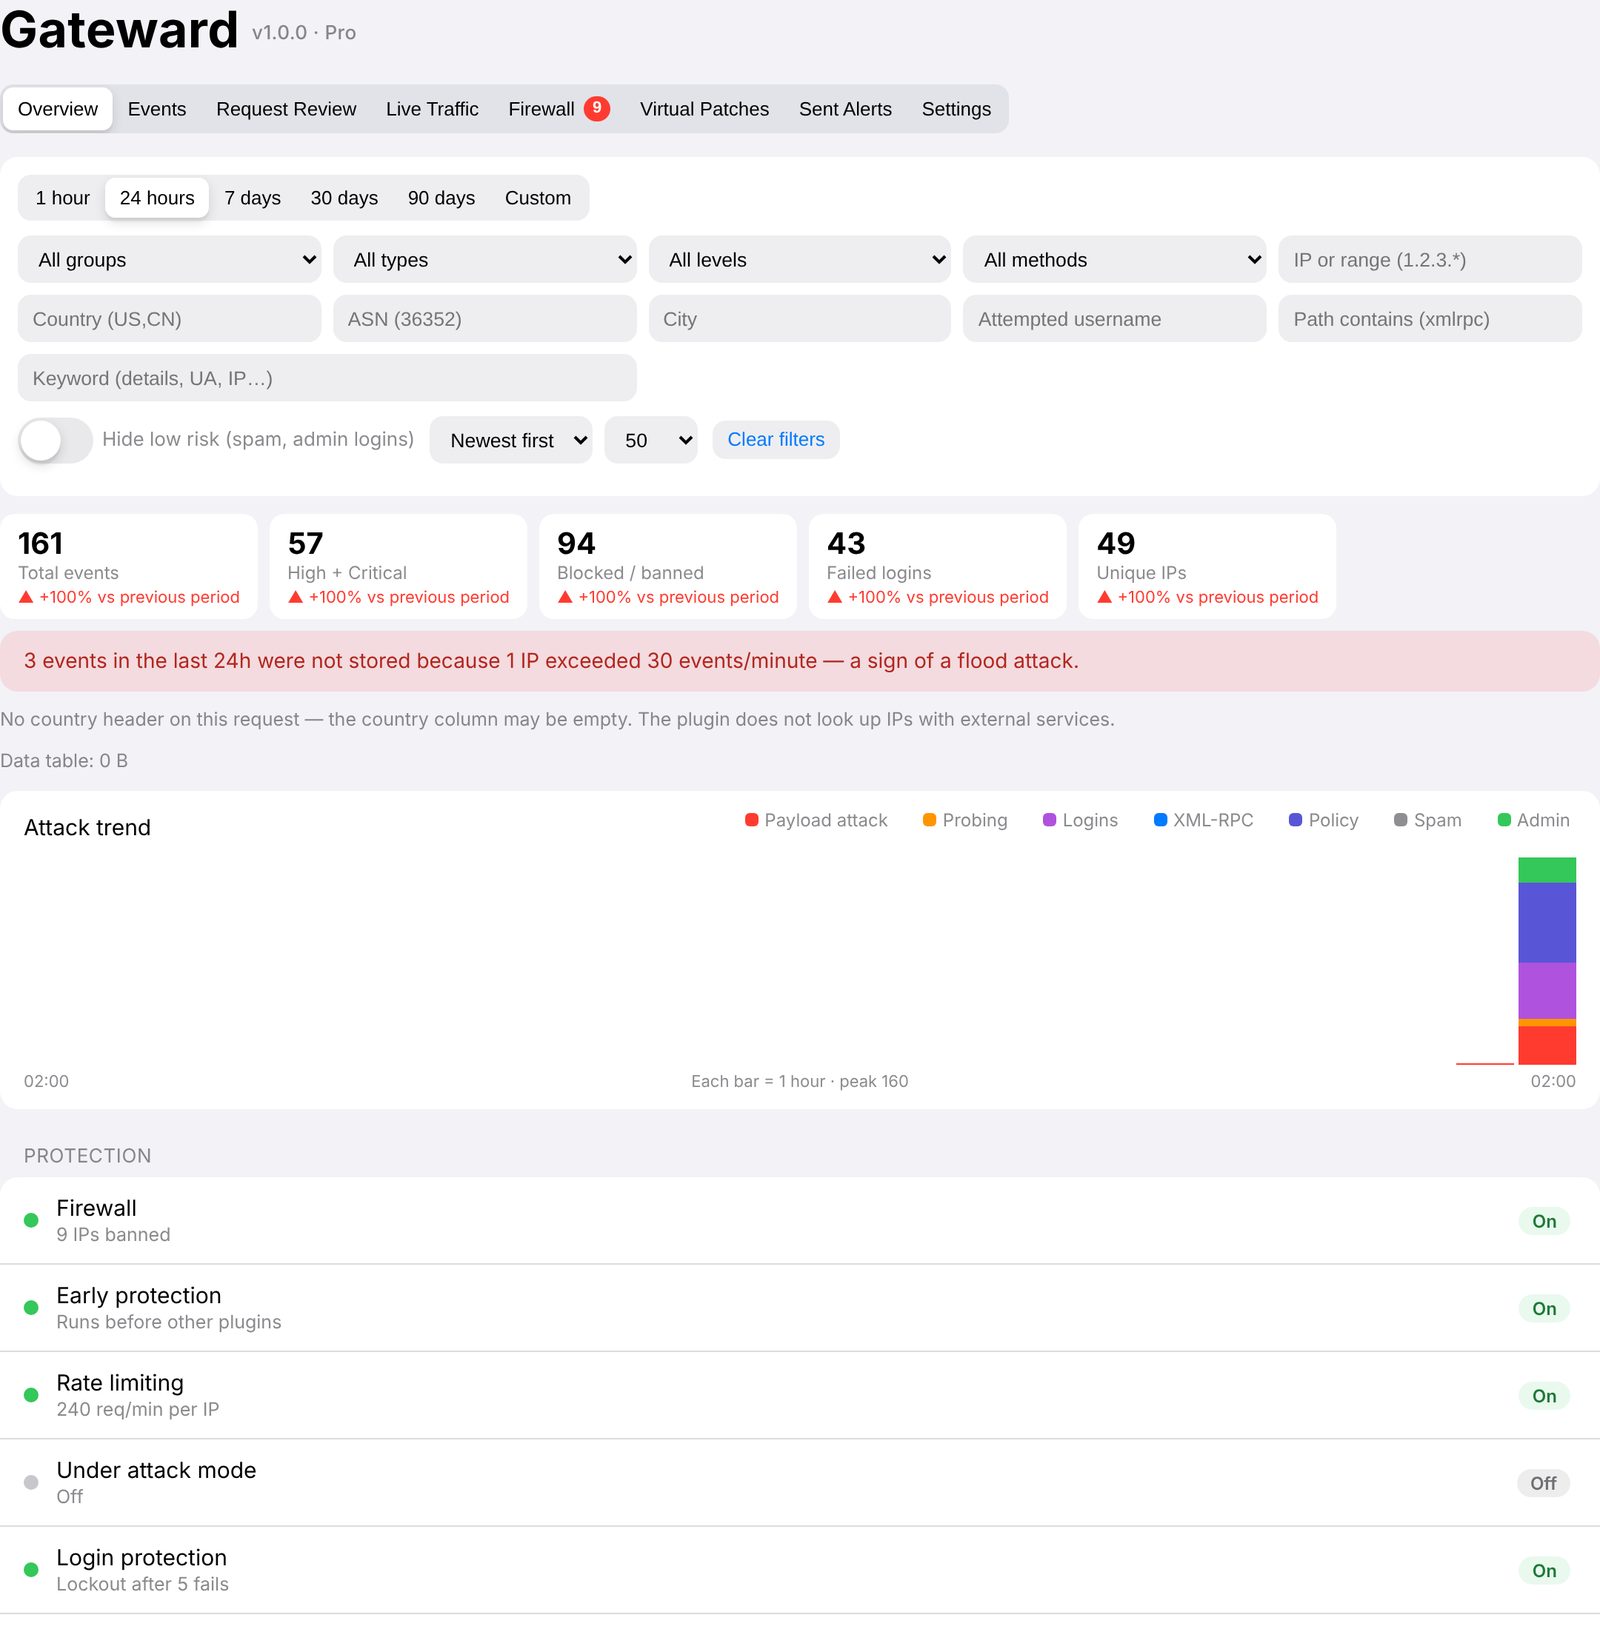
Humans, crawlers and attacks in one stream. Ban an IP or open the route in Request Review in one click.
Questions
Before you install
Can Gateward lock me out?
Logged-in editors and administrators are never blocked, you can't ban your own IP, and banned IPs can still open the login page. If you set a custom login address and forget it, rename the plugin folder over FTP.
Does it work behind Cloudflare or another CDN?
Yes. Choose the matching header in Settings → Network & data so Gateward sees the visitor's real IP; country rules use Cloudflare's country header automatically.
Will it slow my site down?
Bans and rate-limit counters live in small indexed tables (APCu or your object cache when available). 20,000 banned IPs add no measurable time to a page load in our tests.
Do I still need a scanner?
Yes — a firewall stops attacks, a scanner finds the weak spots they target. Codeward is our scanner; the two work side by side.
Put a gate in front of WordPress
Free on WordPress.org. Pro from $59 a year, 14-day money-back guarantee.